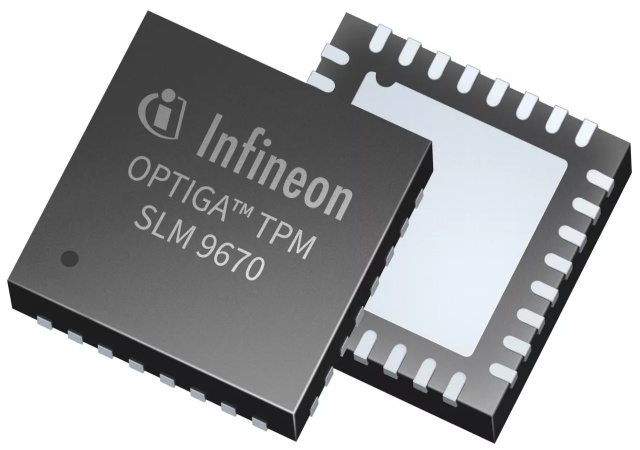
Manufacturer: Infineon Technologies
Key Specifications
- Package: VQFN-32
- Core: 16-bit (to be verified)
- Memory: NVM (size to be verified)
- Interface: SPI (to be verified)
- Voltage: 3.3V (to be verified)
- Temperature: -40°C to 85°C (industrial, to be verified)
- Standard: TPM 2.0 (to be verified)
The SLM9670AQ20FW1311XTMA1 from Infineon Technologies is a dedicated Trusted Platform Module (TPM) security controller designed for industrial applications. It provides a hardware-based root of trust, enabling secure boot, key storage, and platform integrity verification in embedded systems.
Key Features
- Complies with TPM 2.0 specification (to be verified)
- Industrial temperature range support (to be verified)
- Compact VQFN-32 package for space-constrained designs
- Secure non-volatile memory for key and certificate storage
- Standard serial interface for easy integration (SPI or I2C, to be verified)
- Robust cryptographic algorithms for authentication and encryption
Applications
- Industrial PCs and controllers
- Network equipment and edge computing devices
- Medical devices requiring security compliance
- Smart energy and building automation systems
- Any embedded system requiring secure boot and remote attestation
Selection Guidance
When selecting this TPM, verify the exact interface and voltage requirements of your host system. The industrial temperature rating makes it suitable for harsh environments. Confirm the firmware version and certification details with Infineon documentation to ensure compliance with your security standards.